Header image: network cables on a switch. Photo: Kevin Ku / Pexels.
Cloudflare MCP product servers stopped serving /sse on October 22, 2026. A request to the old path returns 410 Gone, and the response points at the server’s /mcp URL. Most MCP clients surface that URL in the connection error. If Cursor, Claude, Windsurf, VS Code, or another client still has …/sse in its config, tools fail until you change the path and sign in again.
This is a URL swap, not a product sunset. Connections that already use /mcp are unaffected. A second Cloudflare change landed the same day—cloudflared URL path normalization—with a different default date of 2027-01-25. Mixing those two into one “Cloudflare broke MCP” story will waste your morning. This piece separates who breaks, what the 410 looks like, the exact /sse → /mcp steps, and when tunnel path rules need a separate re-test.
Note (October 26, 2026): Facts below are from Cloudflare’s MCP
/sseretirement changelog and cloudflared path-normalization changelog, plus the product MCP servers docs as read today./sse→ 410 has been live since October 22, 2026. Path normalization stays off by default until newcloudflaredreleases flip it on 2027-01-25.
Who this bites
You are in scope if an MCP client talks to a Cloudflare product-specific MCP server over a URL that still ends in /sse. Cloudflare’s docs list those servers as optional, targeted endpoints—docs search, containers, Browser Run, DEX, CASB, Agents SDK docs—alongside the broader Cloudflare API MCP server at https://mcp.cloudflare.com/mcp.
Typical setups that break:
- Cursor
mcp.json(or Settings → MCP) with a Cloudflare docs / browser / containers URL ending in/sse - Claude Desktop or Claude Code configs that copied an older
/sseexample - VS Code Copilot / other IDE plugins pointed at a historical
*.mcp.cloudflare.com/ssestring - Shared team snippets, Notion runbooks, or bootstrap scripts that still print
/sse - CI or headless agents that store the MCP base URL in env vars and never got the July 2026 Streamable HTTP guidance
You can skip the MCP section if every Cloudflare MCP URL in your clients already ends in /mcp. Cloudflare’s changelog says those connections are not affected.
You are not fixing this by upgrading Wrangler, rotating Workers secrets, or redeploying an app—unless that app is your own MCP server that still exposes /sse as the only path. Product MCP retirement is about Cloudflare-hosted product servers. For Workers-shaped tooling on this site, see Cloudflare Clairic invoice extraction and cf CLI migrating from Wrangler; those are adjacent Cloudflare builder posts, not the 410 fix.
Tunnel operators with path-based Access ingress have a separate calendar item (section below). Hostname-only tunnels without Access-validated path rules are outside that change.
What fails when /sse returns 410
Cloudflare’s product MCP servers now serve only /mcp. Per the October 22 changelog:
- A request to
/ssereturns410 Gone - The 410 response includes the server’s
/mcpURL - Most MCP clients show that URL in their connection error
- If you originally signed in through
/sse, the client asks you to sign in again after the swap
That matches the direction Cloudflare set earlier in 2026. The July 28, 2026 changelog already told operators to prefer /mcp for new connections: historical /sse URLs were aliases for Streamable HTTP, and clients that forced SSE transport needed to switch to Streamable HTTP or automatic detection. October 22 finishes the retirement: /sse is gone, not aliased.
What you see in practice (patterns across clients, not a single lab transcript):
- Tools vanish or show “disconnected” / “failed to connect”
- A red MCP status badge with
410or “Gone” - An error string that already contains the correct
https://….mcp.cloudflare.com/mcp(orhttps://agents.cloudflare.com/mcp) target—read it before you invent a URL - OAuth / sign-in prompts after you save the new path, if the old token was tied to
/sse
What usually does not fail from this change alone:
- Workers, Pages, R2, or DNS that never talked to product MCP
- Local stdio MCP servers (filesystem, git, etc.) with no Cloudflare HTTP URL
- Clients already on
/mcp - Tunnel ingress matching—unless you also have the separate path-normalization work queued
If your “MCP is down” report started the same week as a cloudflared upgrade, check which symptom you have. A 410 from docs.mcp.cloudflare.com is the MCP path retirement. A wrong backend after a path with .. or // is the tunnel story.
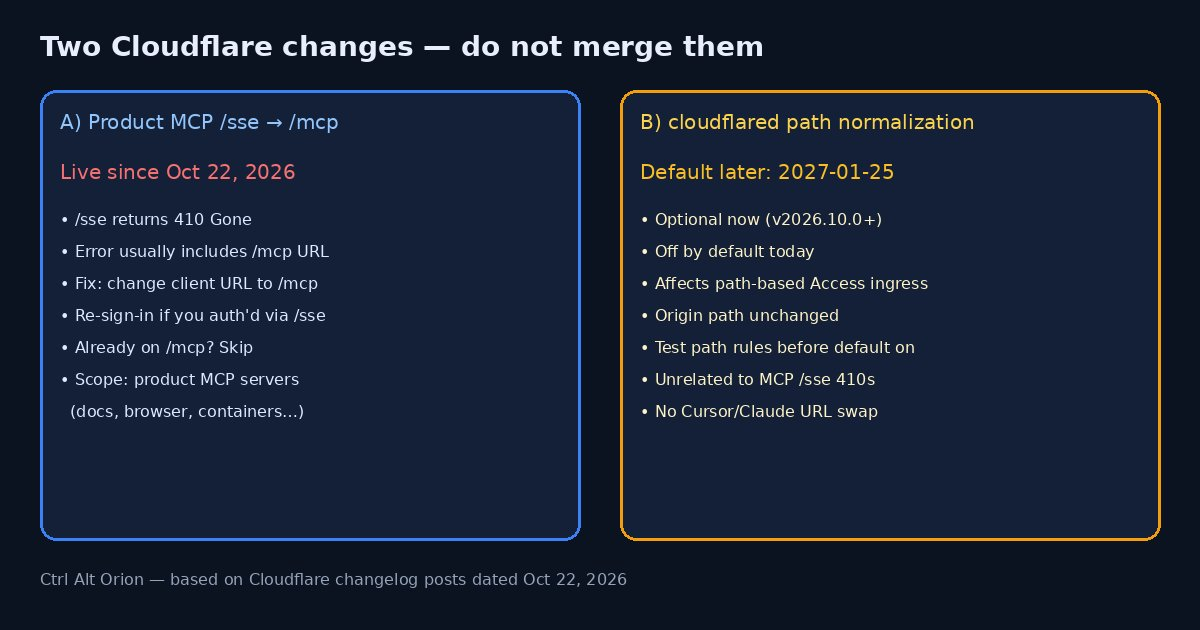 Two dated Cloudflare changes. Diagram: Ctrl Alt Orion. Facts: Oct 22, 2026 changelogs.
Trade-offs and skip-if
The MCP fix is cheap: one path segment and maybe an OAuth round-trip. The cost of delaying is tool outage, not a redesign. Trade-off: if you batch-edit every MCP server in a shared org config, coordinate the re-auth so overnight agents do not reconnect mid-flight with a half-updated secret.
Skip the MCP work when every Cloudflare URL already ends in /mcp. Skip tunnel normalization work when you have no path-based Access-validated ingress. Do both only if both inventories say yes—and keep the tickets dated differently (this week vs before 2027-01-25).
Switch steps: /sse → /mcp
Decision: if config still has /sse, change it to /mcp and re-sign-in. Skip if already on /mcp.
1. Inventory every Cloudflare MCP URL
Search the machines and repos that run agents:
# Examples — adjust roots to your shop
rg -n 'mcp\.cloudflare\.com|/sse' ~/.cursor ~/.claude ~/.config 2>/dev/null
rg -n 'mcp\.cloudflare\.com|/sse' .vscode mcp.json .cursor 2>/dev/null
Look for hostnames like:
| Server (from Cloudflare docs) | Current /mcp URL |
|---|---|
| Documentation | https://docs.mcp.cloudflare.com/mcp |
| Containers | https://containers.mcp.cloudflare.com/mcp |
| Browser Run | https://browser.mcp.cloudflare.com/mcp |
| Digital Experience Monitoring | https://dex.mcp.cloudflare.com/mcp |
| Cloudflare One CASB | https://casb.mcp.cloudflare.com/mcp |
| Agents SDK docs | https://agents.cloudflare.com/mcp |
| Cloudflare API MCP (Code Mode) | https://mcp.cloudflare.com/mcp |
Cloudflare’s example swap in the changelog is exactly that docs URL: change …/sse to https://docs.mcp.cloudflare.com/mcp. The same one-segment edit applies to the other product hosts.
2. Edit the client config
Cursor (common shape; key names vary by version):
{
  "mcpServers": {
    "cloudflare-docs": {
      "url": "https://docs.mcp.cloudflare.com/mcp"
    }
  }
}
VS Code uses a servers root (not mcpServers) and often "type": "http":
{
  "servers": {
    "cloudflare-api": {
      "type": "http",
      "url": "https://mcp.cloudflare.com/mcp"
    }
  }
}
Copy-pasting a Cursor block into VS Code silently does nothing—wrong root key. Cloudflare’s VS Code agent-setup page calls that out.
Claude Desktop / other JSON MCP hosts: same idea—replace the trailing /sse with /mcp, keep the host, save, restart the client if it caches server lists.
Prefer Streamable HTTP / automatic transport. Do not force legacy SSE transport against Cloudflare product servers; that transport is what /sse used to advertise.
3. Re-authenticate when asked
If you signed in through /sse, expect a fresh OAuth / Cloudflare authorize pass after the URL change. Grant the scopes you actually need. For automation, Cloudflare documents API tokens as bearer auth on the API MCP server; product-server OAuth still follows whatever your client already used.
4. Confirm tools list
Reconnect and confirm the server shows connected and tools/resources appear. Hit a cheap read (docs search, list something non-destructive) before you let an agent write DNS or Workers config.
5. Update shared docs
Replace /sse in internal runbooks and onboarding gists the same day. One stale Notion snippet recreates the outage for the next hire.
For building your own remote MCP shape (stateless HTTP, solo-builder constraints), use the separate stateless MCP solo builder guide—that is about your server design, not Cloudflare’s product URL retirement.
Don’t confuse this with cloudflared URL normalization
Same publish day, different product, different deadline.
Product MCP /sse retirement | cloudflared path normalization | |
|---|---|---|
| Changelog date | Oct 22, 2026 | Oct 22, 2026 |
| What changed | /sse → 410 Gone; use /mcp | Optional URL normalize before ingress match |
| Status now | Live | Off by default in 2026.10.0+ |
| Default flip | N/A (already retired) | New releases default on starting 2027-01-25 |
| Who cares | MCP clients with /sse URLs | Tunnels with path-based rules that require Access validation |
| Fix | Edit MCP URL; re-auth | Test path rules; opt in early with --disable-path-normalization=false |
| Origin path | N/A | Unchanged — matching path can differ from origin path |
From the tunnel changelog and config docs:
- Starting in
cloudflared2026.10.0, tunnels can normalize URLs before matching ingress rules - Normalization improves security for rules that require Cloudflare Access validation
- The path sent to your origin stays the same
- Normalization removes RFC 3986 dot segments (
./..), converts backslashes to forward slashes, and merges repeated slashes - Example: incoming
/hello/../pathmatches as/path, but origin still receives/hello/../path - Configurations without rules requiring Access validation are unaffected
- Enable early:
cloudflared tunnel --disable-path-normalization=false run <TUNNEL_NAME_OR_UUID>
or setTUNNEL_DISABLE_PATH_NORMALIZATION=falseon each replica and restart
Before 2027-01-25, re-test any path regex or path-prefix ingress that sits behind Access. Use cloudflared tunnel ingress rule <url> to see which rule wins with normalization on. Hostname-only catch-alls without Access path validation are not the target audience.
Calendar mindset for dated cutovers (different vendor, same discipline): GPT-4o API shutdown migration. Put MCP 410s on this week’s list; put tunnel path dry-runs on a Q4/early-Q1 checklist—not in the same panic ticket.
What shops hit
Patterns shops hit (composites, not claimed as one person’s log):
- A laptop still worked because Cursor was already on
/mcp; the desktop Claude config still had/ssefrom a 2025 gist - The error toast already printed the correct
/mcpURL—operators who ignored it spent longer than the edit required - Team CI failed first: a secret
MCP_DOCS_URL=…/ssein GitHub Actions never got the human OAuth prompt, only a hard 410 - Someone “fixed” tunnel Access after reading the wrong Oct 22 changelog and never touched MCP config
Checklist
MCP (do now if still on /sse):
- Search configs for
mcp.cloudflare.comand/sse - Replace
/ssewith/mcpon each product server URL - Prefer Streamable HTTP / auto transport; do not force SSE
- Re-sign-in when the client asks
- Confirm tools reconnect with a read-only probe
- Patch shared snippets / onboarding docs
- Skip entirely if every URL already ends in
/mcp
Tunnel path normalization (separate; before 2027-01-25 if in scope):
- Confirm you run path-based ingress that requires Access validation
- On a canary replica, enable normalization (
--disable-path-normalization=falseor env) - Exercise paths with
..,//, and\that your rules care about - Compare
cloudflared tunnel ingress ruleresults before vs after - Remember origin still receives the un-normalized path
- Skip if you have no Access-validated path rules
Skip-if summary: Already on /mcp → no MCP work. No Access path rules → no tunnel normalization work. Do not open both tickets as one outage.
FAQ
When did Cloudflare MCP /sse stop working?
October 22, 2026. Product-specific MCP servers return 410 Gone on /sse and advertise the /mcp URL. The change is already live as of this article’s date (October 26, 2026).
What URL should I use instead?
Use the same host with /mcp. Cloudflare’s documented example is https://docs.mcp.cloudflare.com/mcp. Other product hosts follow the same pattern; the API MCP server is https://mcp.cloudflare.com/mcp.
Do I need to re-authenticate?
If you signed in through /sse, yes—the client will ask you to sign in again after you switch to /mcp. Connections that were already on /mcp stay as they are.
Is this the same as the cloudflared path-normalization change?
No. Path normalization is a Tunnel/cloudflared feature for matching ingress rules (especially with Access). It is optional now and defaults on in new releases starting 2027-01-25. It does not retire MCP /sse.
Will my origin see a different path after normalization?
No. Cloudflare states the URL path sent to your origin stays the same. Only the path used for ingress matching is normalized when the feature is on.
Who is unaffected by path normalization?
Configurations without rules that require Access validation. Hostname-only routing without those Access path checks is outside the change’s stated impact.
Does the Cloudflare API MCP server still work?
Yes. Docs present https://mcp.cloudflare.com/mcp as the primary Code Mode / full-API server. Use /mcp. Treat any leftover /sse string like the product servers: swap and re-auth if needed.
I build my own MCP server on Workers—must I remove /sse?
This changelog targets Cloudflare’s product-specific MCP servers. Your own Worker can still choose which paths to serve; follow current Agents / Playwright MCP guidance for Streamable HTTP. Prefer /mcp for new clients so you are not teaching a dead transport.
Where is the official swap example?
Cloudflare’s MCP retirement changelog and the product MCP servers page both point at /mcp endpoints such as https://docs.mcp.cloudflare.com/mcp.
Sources
7 refs- Cloudflare Changelog, “Cloudflare MCP servers no longer serve /sse” (October 22, 2026): https://developers.cloudflare.com/changelog/post/2026-10-22-cloudflare-mcp-servers-retire-sse/developers.cloudflare.com
- Cloudflare Changelog, “Cloudflare Tunnel supports URL normalization” (October 22, 2026): https://developers.cloudflare.com/changelog/post/2026-10-22-cloudflared-path-normalization/developers.cloudflare.com
- Cloudflare Docs, “Cloudflare’s own MCP servers” (product URLs at
/mcp): https://developers.cloudflare.com/agents/model-context-protocol/cloudflare/servers-for-cloudflare/developers.cloudflare.com - Example
/mcpendpoint referenced in changelog: https://docs.mcp.cloudflare.com/mcpdocs.mcp.cloudflare.com - Cloudflare Docs, tunnel configuration / how traffic is matched (normalization behavior): https://developers.cloudflare.com/tunnel/features/locally-managed-tunnels/configuration-file/developers.cloudflare.com
- Cloudflare Changelog, “Cloudflare MCP servers support the new MCP 2026-07-28 Specification” (July 28, 2026 — prefer
/mcp;/sseas historical alias): https://developers.cloudflare.com/changelog/post/2026-07-28-cloudflare-mcp-servers-mcp-2026-07-28/developers.cloudflare.com - Cloudflare Docs, Visual Studio Code agent setup (HTTP MCP config shape): https://developers.cloudflare.com/agent-setup/visual-studio-code/developers.cloudflare.com
comments
loading comments…
No comments yet. Start the thread.